x



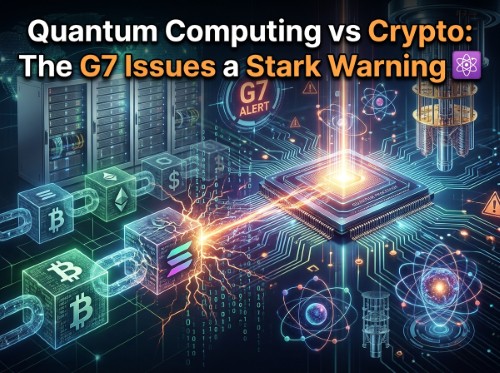
The debate surrounding quantum computing has officially shifted from theoretical physics to immediate digital security. In a sobering report released by the Group of Seven (G7) Cybersecurity Working Group—representing Canada, France, Germany, Italy, Japan, the United Kingdom, and the United States—governments and commercial enterprises have been urged to begin transitioning to post-quantum cryptography (PQC) without delay.
While quantum computers capable of shattering modern encryption may still be years away, the window to safeguard critical digital infrastructure is rapidly closing. The threat is not merely a problem for tomorrow; it is a vulnerability being actively exploited today.
To understand why the G7 is taking such an urgent stance, one must look at how cyber adversaries operate. The primary tactic causing concern among intelligence agencies is known as "harvest now, decrypt later" (HNDL).
Sophisticated threat actors and state-sponsored groups are actively intercepting and storing vast volumes of encrypted communications, financial records, and proprietary data. Whilst today’s classical computers cannot crack this information, future quantum machines running Shor’s algorithm will easily dismantle standard RSA and Elliptic Curve Cryptography (ECC) frameworks.
When that milestone is reached, any data harvested today will be decrypted in seconds. This puts national security secrets, private personal data, and corporate supply chains at severe long-term risk.
Although the G7 report focuses broadly on national infrastructure and enterprise resilience, the cryptocurrency and blockchain ecosystem sits squarely in the line of fire. Modern decentralised networks rely almost entirely on public-key cryptography to generate wallet addresses, authorise transactions, and maintain ledger integrity.
If a quantum computer were able to derive private keys from public keys, the foundational trust underpinning public blockchains would collapse. Recognising this existential threat, core developers across major protocols are already testing defensive measures.
Bitcoin's Governance Challenge
Bitcoin relies on Secp256k1 elliptic curve cryptography. While current quantum devices cannot breach it, updating the Bitcoin network is notoriously complex due to its decentralised governance model. Any fundamental cryptographic alteration requires widespread consensus among developers, miners, node operators, and businesses.
Proposals such as BIP-360 aim to prepare the Bitcoin network for quantum resilience by introducing support for alternative, quantum-safe signature schemes. However, migrating unspent transaction outputs (UTXOs)—especially dormant coins held in older address formats—presents a colossal operational hurdle that will demand years of coordinated planning.
Ethereum's Cryptographic Overhaul
Ethereum researchers are taking a proactive stance by designing quantum-resistant upgrades for accounts, validator operations, and smart contracts. Recent research focusses on updating the Ethereum deposit contract to support the larger key sizes required by post-quantum signature schemes. Given Ethereum's modular design and active upgrade cadence, integrating quantum safety into future network roadmaps remains a top priority.
Solana's Flexible Architecture
Solana, which utilises EdDSA (Edwards-curve Digital Signature Algorithm), may benefit from a smoother migration path. Developers have already commenced testing post-quantum signature schemes on test networks and have introduced optional hash-based cryptographic vaults to protect user assets against quantum-level exploits.
To comprehend how blockchains will withstand quantum attacks, it is essential to examine the underlying mathematics that make post-quantum cryptographic primitives secure against quantum algorithms.
Classical blockchains rely heavily on two mathematical puzzles: the Discrete Logarithm Problem and Integer Factorisation. Shor’s algorithm solves both in polynomial time using quantum Fourier transforms. Post-quantum algorithms, by contrast, rely on mathematical problems for which no known quantum algorithm offers an exponential speed-up.
1. Lattice-Based Cryptography
Lattice-based algorithms represent the frontrunner for post-quantum security and have been heavily standardised by NIST (National Institute of Standards and Technology).
The Core Mathematical Problem: Rather than operating on numbers along an elliptic curve, lattice cryptography relies on high-dimensional geometric structures called lattices. Security is anchored in problems such as Learning With Errors (LWE) and the Shortest Vector Problem (SVP)—finding the closest point in an $n$-dimensional grid filled with high noise levels.
Primary Algorithms:
ML-DSA (formerly Dilithium): A lattice-based digital signature scheme that replaces ECDSA and Ed25519. It provides strong security and fast computation, making it ideal for validating blockchain transactions.
Falcon: Another lattice scheme offering smaller signature sizes, though it relies on complex floating-point mathematics during signing.
Blockchain Application: Blockchains can swap ECDSA validation logic with ML-DSA to ensure that transaction signatures cannot be forged by a quantum computer.
2. Stateless Hash-Based Cryptography
Hash-based cryptography offers one of the most mathematically conservative approaches to quantum resistance because its security relies entirely on collision-resistant hash functions (such as SHA-256 or SHAKE-256).
The Core Mathematical Resilience: While quantum computers can use Grover’s algorithm to speed up searches against hash functions, Grover’s algorithm only offers a quadratic speedup (effectively halving the bit-security level). Doubling the hash output size—from 128-bit equivalent to 256-bit—completely neutralises Grover's advantage.
Primary Algorithm: SLH-DSA (formerly SPHINCS+). This stateless hash-based signature scheme links thousands of one-time signature schemes into a tree-like hierarchy (Merkle tree structures).
Blockchain Application: Because hash functions are already deeply integrated into blockchain consensus (such as Proof of Work and Merkle roots), hash-based signatures are regarded as the safest long-term fallbacks for high-value wallet vaults.
3. The On-Chain Trade-Offs: Size, Speed, and Gas Costs
Migrating a blockchain to post-quantum signatures is not merely a matter of changing a few lines of code; it introduces significant technical trade-offs:
Signature and Public Key Bloat: A classical ECDSA signature is roughly 64 bytes, and its public key is 33 bytes. In contrast, an ML-DSA signature ranges between 2.4 KB and 4.6 KB, while a SPHINCS+ signature can exceed 7 KB to 40 KB.
Network Throughput and Storage: Incorporating signatures that are 40 to 100 times larger means fewer transactions fit into a single block. This leads to higher gas fees, network congestion, and substantial state bloat for full node operators.
Crypto-Agility and Account Abstraction: To mitigate these challenges, developers are using Account Abstraction (such as ERC-4337 on Ethereum). Account abstraction separates the transaction validation logic from the core protocol layer, allowing individual smart contract wallets to experiment with quantum-resistant signature schemes (or batch multiple quantum signatures via zero-knowledge proofs) without requiring an immediate, disruptive hard fork of the entire network.
Transitioning global digital systems and blockchain networks to post-quantum standards will be one of the largest technological migrations in human history. The G7 stresses that individual organisations and decentralised communities cannot handle this transition in isolation.
To prepare effectively, enterprise teams and protocol builders should adopt a three-step strategy:
Perform a Cryptographic Inventory: Identify all legacy encryption algorithms, digital signatures, and public keys currently deployed across internal and external systems.
Prioritise High-Value Assets: Focus immediate defensive measures on long-term confidential data and asset vaults that must remain secure over a multi-decade horizon.
Embrace Crypto-Agility: Build software architectures and smart contracts that allow cryptographic algorithms to be swapped or upgraded dynamically as quantum standards mature.
The transition to post-quantum cryptography is no longer a distant line item on a future roadmap. It is an immediate imperative for any organisation looking to secure the digital economy of tomorrow.
Disclaimer: This article is provided for informational purposes only, mistakes may be made, and it's not offered or intended to be used as legal, tax, investment, financial, or any other advice.