x



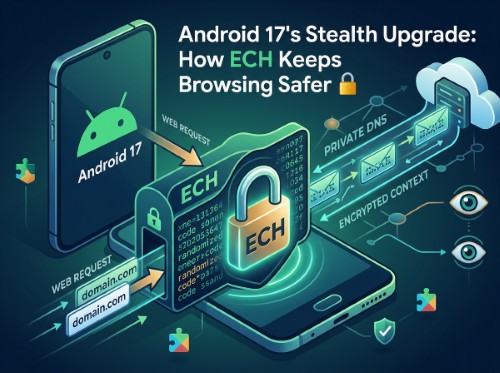
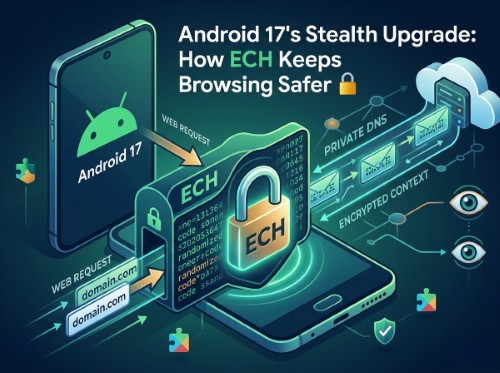
Digital privacy has taken a substantial step forward with the arrival of Android 17. Google’s latest mobile operating system introduces platform-level support for Encrypted Client Hello (ECH)—a vital network security standard designed to seal one of the last remaining open vulnerabilities in web traffic encryption.
While HTTPS has long scrambled the actual contents of the web pages you visit, the specific domain name you were accessing often remained visible to middle-tier observers. With Android 17, Google aims to plug this privacy gap, though understanding how ECH works reveals why your online activity isn't fully hidden just yet.
To understand why ECH is such a milestone, it helps to examine how connection handshakes work.
When you open a secure website, your browser uses HTTPS to encrypt sensitive data like passwords, payment details, and personal communications. However, before that encrypted tunnel is established, your device must negotiate a initial connection with the target server.
During this initial handshake, a cleartext field called Server Name Indication (SNI) is transmitted. The SNI explicitly tells the destination server which website domain you are trying to reach. Because this specific field travels unencrypted, anyone monitoring the network path—including mobile phone carriers, broadband Internet Service Providers (ISPs), public Wi-Fi administrators, or malicious network eavesdroppers—can log every single domain name you attempt to visit.
Even if you use Private DNS (such as DNS-over-HTTPS) to prevent ISPs from logging your DNS lookups, the plain-text SNI field during the TLS handshake still exposes your destination.
Encrypted Client Hello, developed in collaboration with Google's Jigsaw team and outside security engineers, neutralises this loophole.
Under ECH, your Android device encrypts the SNI payload using a public key previously published by the destination web server. When the request travels across the internet:
By integrating ECH into Android 17 by default, Google provides the first broad implementation of this security standard across a major mobile platform.
While ECH represents a dramatic leap forward for network-level privacy, it is not a complete cloak of invisibility. There are two key limitations users must keep in mind:
1. Server-Side Adoption is Still Required
ECH only functions if the destination website or app infrastructure explicitly supports it. If you attempt to access a server that has not enabled ECH compatibility, the connection reverts to standard protocols, exposing the domain name in cleartext. To accelerate adoption, Google is actively urging app developers to update their networking libraries to OkHttp 5.5.0 or later and activate ECH support.
2. IP Addresses and Traffic Metadata Remain Visible
ECH protects the domain name label, but it cannot alter the fundamentals of how routing works on the internet. Network observers can still see:
On servers hosting a single website, sophisticated observers can easily deduce where you are going simply by cross-referencing the destination IP address. However, on multi-tenant servers or content delivery networks (CDNs) hosting thousands of domains behind a single IP address, ECH renders individual user tracking significantly harder.
The rollout of ECH is part of a broader push to tighten device and network security in Android 17. Alongside ECH support, the operating system introduces:
These network adjustments arrive alongside an evolving conversation around smartphone privacy at the hardware and operating system level, as demonstrated by recent high-profile legal debates regarding hardened custom Android builds like GrapheneOS and user data ownership.
Android 17’s implementation of Encrypted Client Hello marks a crucial step towards closing long-standing privacy loopholes on the internet. While it does not replace the comprehensive anonymisation offered by virtual private networks (VPNs) or multi-hop tools like Tor, ECH ensures that baseline mobile browsing becomes substantially more secure against passive network monitoring.
Disclaimer: This article is provided for informational purposes only, mistakes may be made, and it's not offered or intended to be used as legal, tax, investment, financial, or any other advice.