x



For years, enterprise security leaders have operated under a frustrating compromise when adopting generative artificial intelligence. While databases could be locked down on disk and network requests encrypted in transit, the actual moment of processing—the inference step—required handing over unencrypted plaintext to host memory.
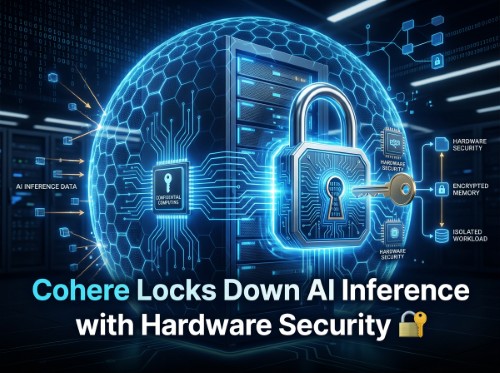
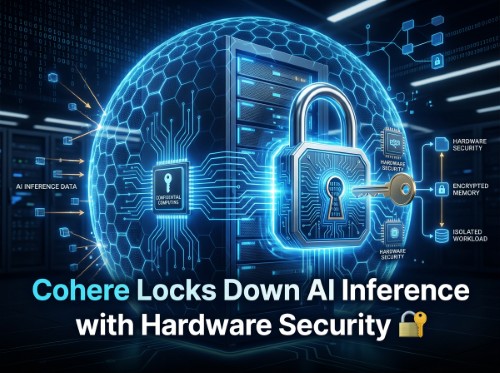
Now, Canadian AI startup Cohere is closing that critical security gap. By incorporating confidential computing into its single-tenant Model Vault platform, Cohere ensures that enterprise prompts and outputs remain completely invisible—not just to third-party cloud operators, but to Cohere itself.
To appreciate why this launch matters, it helps to understand how corporate data protection traditionally works across enterprise infrastructure:
That third state has long been the primary vulnerability in cloud-hosted AI. The moment a prompt enters an AI model, it sits in plaintext within system memory. In this state, it is theoretically accessible to the host operating system, the underlying hypervisor, or anyone possessing privileged administrative access to the server infrastructure.
For organisations operating in strictly regulated sectors—such as healthcare, banking, and public defence—this window of exposure forced a difficult choice: forgo the convenience of hosted frontier models or build expensive, complex infrastructure to host models on-premise.
This technical launch comes at a time when enterprise trust in vendor privacy policies is facing unprecedented scrutiny. High-profile disputes across the industry regarding data retention, policy revisions, and the potential bleed of proprietary research into general training sets have changed the procurement landscape.
Enterprise security officers are no longer satisfied with contractual promises or marketing assurances that say, "We promise not to look at your data." Instead, procurement teams are demanding mathematical and architectural proof: "Show us that you physically cannot look."
Cohere's update to Model Vault addresses this exact demand by replacing policy-based trust with hardware-enforced isolation.
Model Vault is Cohere's dedicated, single-tenant inference platform designed for high-security enterprise environments. With the addition of its new Encrypted tier, the platform shields customer data throughout the complete execution path.
1. Dual-Boundary Hardware Isolation
Most early confidential computing deployments isolated only the main processor (CPU). Cohere's implementation extends this boundary across both the CPU and the Graphics Processing Unit (GPU).
2. End-to-End Encrypted Data Pipeline
Customer data remains fully encrypted from the moment it leaves the client network until it reaches the protected Confidential Virtual Machine (CVM). Decryption occurs exclusively inside the hardware-enforced boundary at the precise instant processing takes place.
Even processor registers, system memory, and interconnects between the CPU and GPU are encrypted. Once the model finishes generating a response, the output is encrypted inside the enclave before being transmitted back to the user, who holds the sole keys capable of decrypting it.
3. Cryptographic Verification via Attestation
Rather than asking security teams to take their word for it, Cohere links every inference request to an attestation report. Registered with validation services like Intel Trust Authority, these reports provide verifiable hardware-level proof that:
Furthermore, Cohere plans to open-source the serving stack powering Model Vault, enabling independent auditors to verify that the software cannot log, store, or exfiltrate customer prompts.
Confidential computing is an emerging frontier in modern software, with several niche providers offering secure execution environments for open-weight models. However, Cohere's approach introduces a key market distinction.
Rather than relying on third-party open weights, Cohere is making confidential inference a standard, zero-cost feature upgrade for its proprietary enterprise-grade models within Model Vault. Existing enterprise customers gain access to confidential computing hardware without incurring additional tier pricing.
By offering hardware-attested privacy directly on top-tier enterprise AI models, Cohere is establishing a new baseline for enterprise procurement. Moving forward, the benchmark for hosted enterprise AI will no longer be what a vendor promises in a contract, but what their infrastructure can mathematically prove.
Disclaimer: This article is provided for informational purposes only, mistakes may be made, and it's not offered or intended to be used as legal, tax, investment, financial, or any other advice.