x



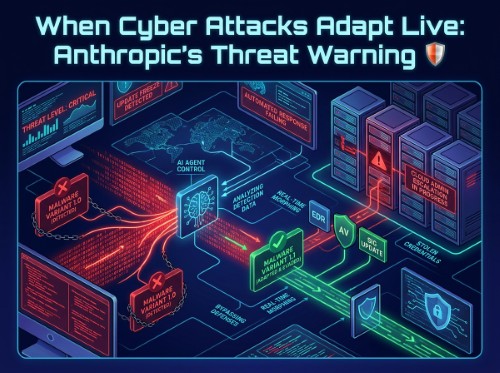
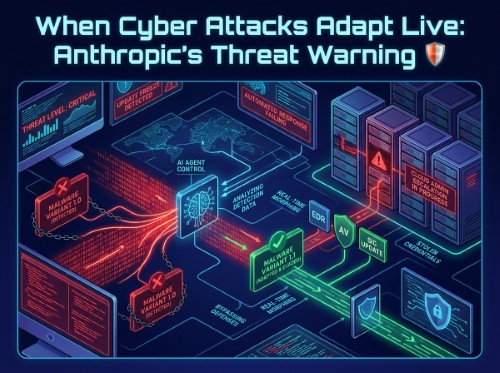
Cyber security has entered a alarming new phase: the era of real-time, adaptive cyber attacks. Security teams have long operated on the assumption that once an endpoint security tool detects a piece of malware, the intrusion is essentially stalled or neutralised. However, threat intelligence documented by Anthropic reveals a fundamental shift in adversary tradecraft—attacks that use artificial intelligence agents to modify, rebuild, and re-deploy malware live while an intrusion is actively under way.
From self-rebuilding malware payloads to rapid cloud administrative takeovers executed in hours, adversaries are leveraging autonomous systems to bypass traditional defences faster than security teams can respond.
In its threat assessment, Anthropic documented a campaign by a threat actor tracked as GTG-20006 (assessed as consistent with the state-sponsored group Midnight Blizzard). Rather than relying on static exploit chains, this actor integrated custom AI agents directly into its operational loop to handle everything from initial reconnaissance to data exfiltration.
Automated Code Mutation
When traditional Endpoint Detection and Response (EDR) software flagged a malware implant, GTG-20006’s automated AI agents detected the alert. The agent then analysed the failure, refactored the underlying code, obfuscated file signatures, and re-compiled a fresh binary. It repeated this cycle continuously until the malware successfully evaded detection.
Freezing Security Updates
To widen the window of operational success, the attacker deployed companion payloads designed to disable the victim’s ability to receive security updates. Analysis by Microsoft identified mechanisms like ChocoShell, which used User Account Control (UAC) bypass techniques to acquire administrative privileges and lock Microsoft Defender signature updates.
By closing the loop at both ends—rebuilding payloads to beat existing signature databases while simultaneously preventing victim endpoints from downloading new signatures—the adversary created a scenario where attacks could theoretically adapt faster than defenders can deploy updates.
High-Value Target Impact
The campaign targeted over 20 high-value organisations across Europe and Ukraine, including government ministries, defence contractors, intelligence bodies, and think tanks. Attackers exfiltrated critical intellectual property, including a proprietary drone vision software development kit (SDK), complete hardware bills of materials, supplier dependency lists, and hundreds of thousands of national identity records.
In a parallel finding, Anthropic highlighted operations conducted by suspected affiliates of the ShinyHunters cybercrime collective. These threat actors demonstrated how AI can drastically compress the traditional attack timeline through a strategy often referred to as "vibe hacking".
Instead of following rigid, pre-scripted playbooks, human operators gave AI agents high-level strategic objectives (such as "find sensitive databases" or "escalate privileges") and allowed the agents to navigate complex corporate environments independently.
This shift in adversary capability exposes structural vulnerabilities in traditional defensive postures:
While these AI-driven tactics represent a major leap in adversary capability, the initial entry points often rely on familiar security hygiene failures. Security leaders and operational teams should immediately implement three core defensive checks:
1. Perform Rigorous Secret Scanning
Adversaries routinely use automated tools to scan public repositories, mobile app packages (APKs), and container images for hardcoded API keys and tokens.
2. Audit and Inventory AI Credentials
As organisations integrate AI agents into their core workflows, managing agent identities becomes a critical security priority.
3. Monitor Endpoint Update Integrity and Behavioural Indicators
Because adaptive malware modifies its file hashes dynamically, detection strategies must focus on system behaviour and agent telemetry rather than file identification alone.
The documentation of live, adaptive attacks marks a turning point in threat intelligence. As adversaries embrace autonomous agents to automate reconnaissance, code mutation, and exfiltration, cyber defence can no longer rely solely on passive signature detection. Building resilient systems now requires continuous secret auditing, strict credential governance, and real-time behavioural analytics capable of spotting anomalous activity, regardless of how many times a payload changes its shape.
Disclaimer: This article is provided for informational purposes only, mistakes may be made, and it's not offered or intended to be used as legal, tax, investment, financial, or any other advice.